Update PHP now, two critical RCE flaws fixed in PHP 8.5.12 and 8.4.27
The PHP project released PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 to fix two critical flaws that allow unauthenticated RCE. Here is how to check your server.
The PHP project released PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026 to fix two critical flaws that can allow unauthenticated remote code execution (RCE). The security notice on php.net urges all PHP users to update immediately. If you run your own PHP site, WordPress on a VPS or a Laravel app, check the PHP version on your server today.
What happened
The flaws are CVE-2026-109618 and CVE-2026-109619. The php.net notice says the first comes from out-of-memory handling that can interrupt PHP while internal request data is only partly set up. The second is internal request state that survives after its backing memory is freed, and a later request handled by the same worker can use it.
According to the notice, every PHP installation that serves web requests is affected, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. The risk is highest for mod_php, where a demonstrated exploit lets an unauthenticated request trigger the attack before any application code runs.
AFP reported that government agencies, media operators and services in Australia, France, the Netherlands and other countries took sites offline as a precaution. The US National Security Agency told organisations to patch immediately or pull vulnerable systems offline. Security firm Wiz estimates PHP runs about 70 per cent of the world's websites.
How to update
- Move to the latest release on your branch: 8.5.12, 8.4.27, 8.3.36 or 8.2.35.
- Linux distributions received the patches in advance, so check your vendor's packages. Shared-hosting users should ask their host whether PHP has been updated.
- PHP 8.1 and older no longer get updates from the PHP project. Some distributions and LTS vendors provide backported fixes, so contact your vendor or upgrade to a supported version.
- If you cannot update right away, the php.net notice lists ways to reduce exposure, such as setting
session.upload_progress.enabled=0and a lowpost_max_size. It stresses that these do not make an installation safe; only an update does.
Who found it
AFP reported that security firm Calif found the flaws in August using OpenAI's GPT-5.6 Sol model, in an OpenAI-funded audit of PHP's code. Wiz, which is owned by Google, said it found them independently weeks later with help from AI models including Google's Gemini 4 Argon and GPT-5.6 Sol. Details leaked online on Tuesday, a day before the planned release of the fix, so the release was brought forward.
A researcher who has worked on PHP issues for Calif told the BBC that exploitation did not look widespread so far, AFP reported. You still should not wait for proof of attacks before updating.
What to do next
Run php -v on your server, and restart PHP-FPM or Apache workers after the upgrade so the new version is the one actually serving requests. We found no statement aimed specifically at Malaysian users at the time of writing; the steps for local administrators are the same as above.
Read also
- Before you share a vibe-coded app, check these four security gaps
- Before you install a Claude skill from GitHub, check these things
- Google announces Gemini 4 Argon, rolling out first to cyber defenders
Sources
- PHP.net, Security advisory: Critical remote code execution vulnerabilities, update now, 21 October 2026
- Malay Mail (AFP), Websites worldwide shut down after critical PHP flaws expose servers to hackers, 22 October 2026
- Malay Mail (AFP), AI just found a giant hole in PHP, and the internet is scrambling, 23 October 2026
- Malay Mail (AFP), Is the website down? What to know about the global PHP security scare, 23 October 2026
The saksama editorial team
Read next
All Tech stories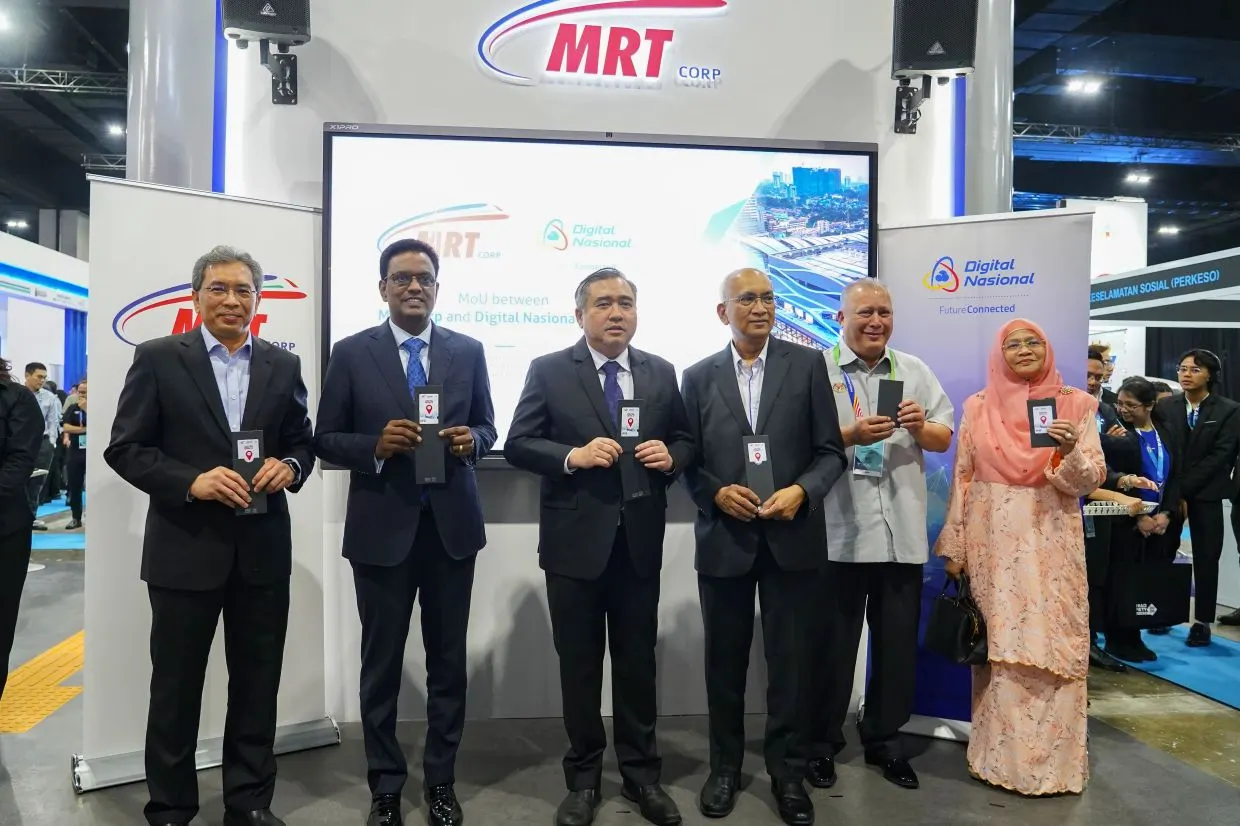
DNB and MRT Corp to bring indoor 5G to the RTS Link complex in Johor Bahru
Digital Nasional Berhad and MRT Corp signed an MoU for indoor 5G at the RTS Link complex in Bukit Chagar. U Mobile signed its own MoU three days later.
Claude skill repos worth a look in October 2026
GitHub repos worth knowing for Claude skills, from Anthropic's official repo to packs for Obsidian and science, with star counts and install commands.
Before you share a vibe-coded app, check these four security gaps
Researchers keep finding the same four mistakes in AI-built apps, and some have leaked personal data. What to check first, and Malaysia's breach rules.